x64dbg vs Ghidra: catalog facts
  x64dbg |  Ghidra |
|---|
| |
|
Best for: Debugging and patching Windows binaries during reverse engineering |
Best for: Reverse engineering a binary when you need a decompiler and cannot pay for IDA |
|
Free Free and open source under the GPLv3. |
Free Free and open source under Apache 2.0, released by the NSA. |
|
Windows |
Windows, macOS, Linux |
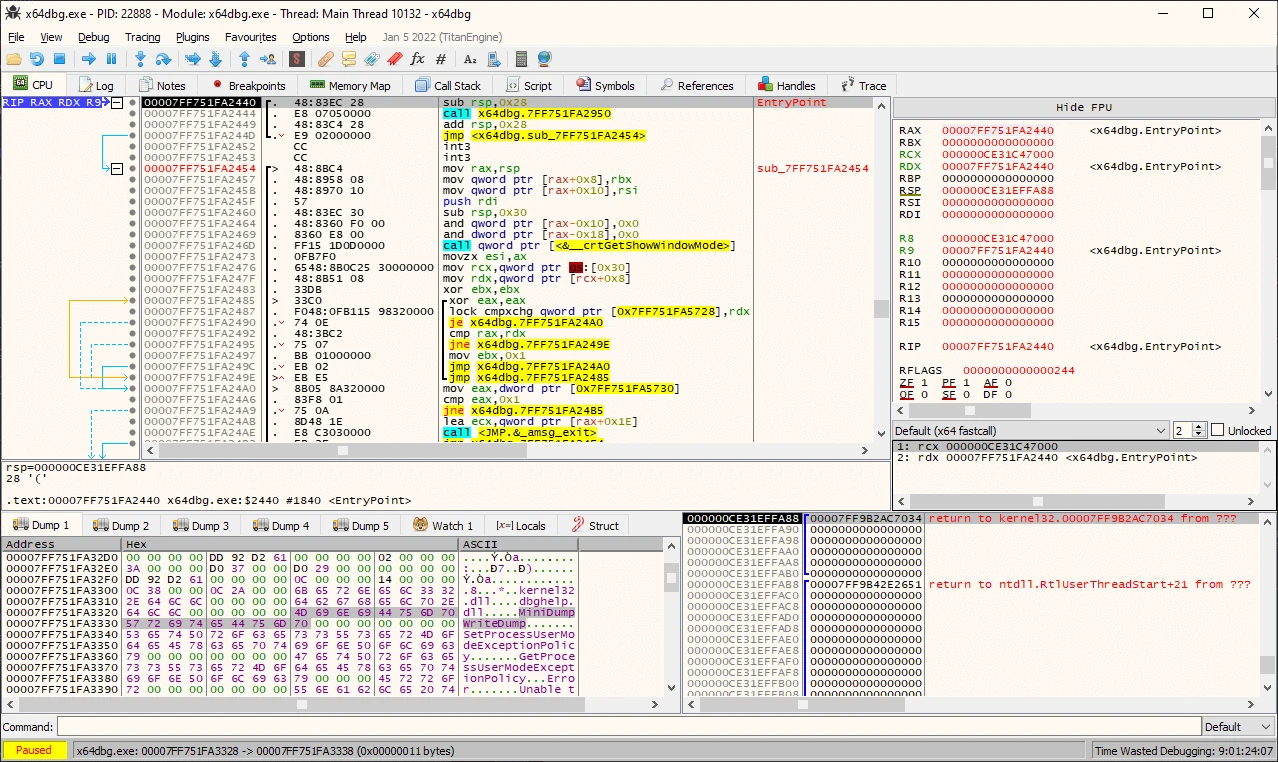
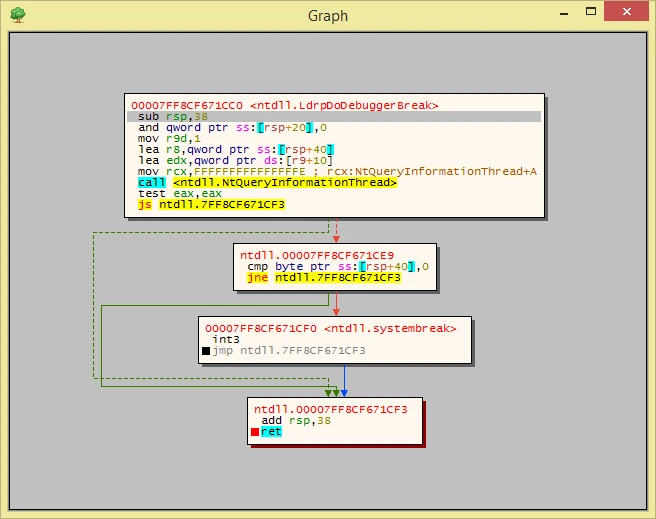
- IDA-like sidebar, jump arrows and token highlighting make it immediately readable
- Import reconstruction with Scylla and a built-in assembler for patching
- Yara pattern matching and a Snowman decompiler included
- A scriptable, debuggable automation language plus a growing plugin API
|
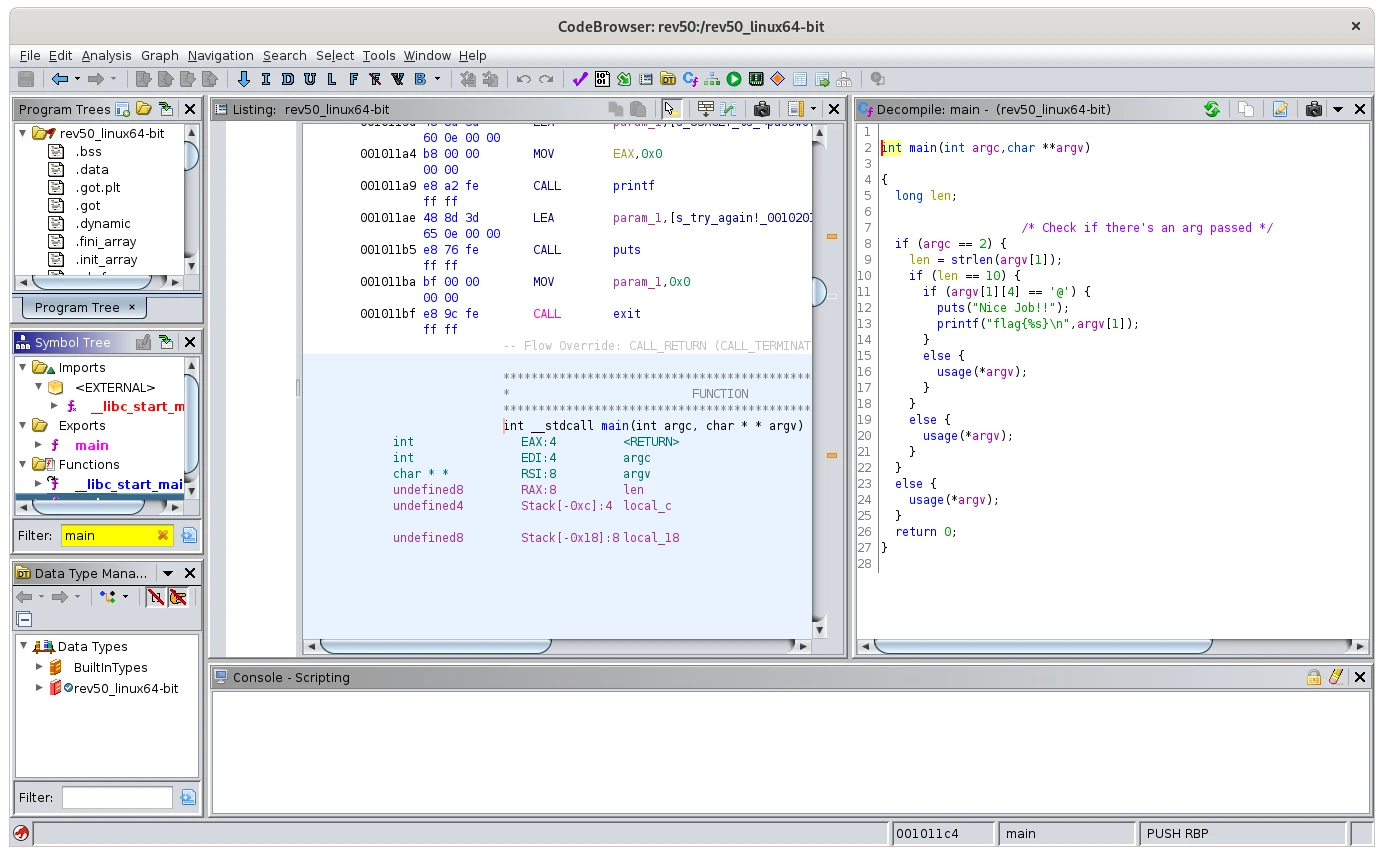
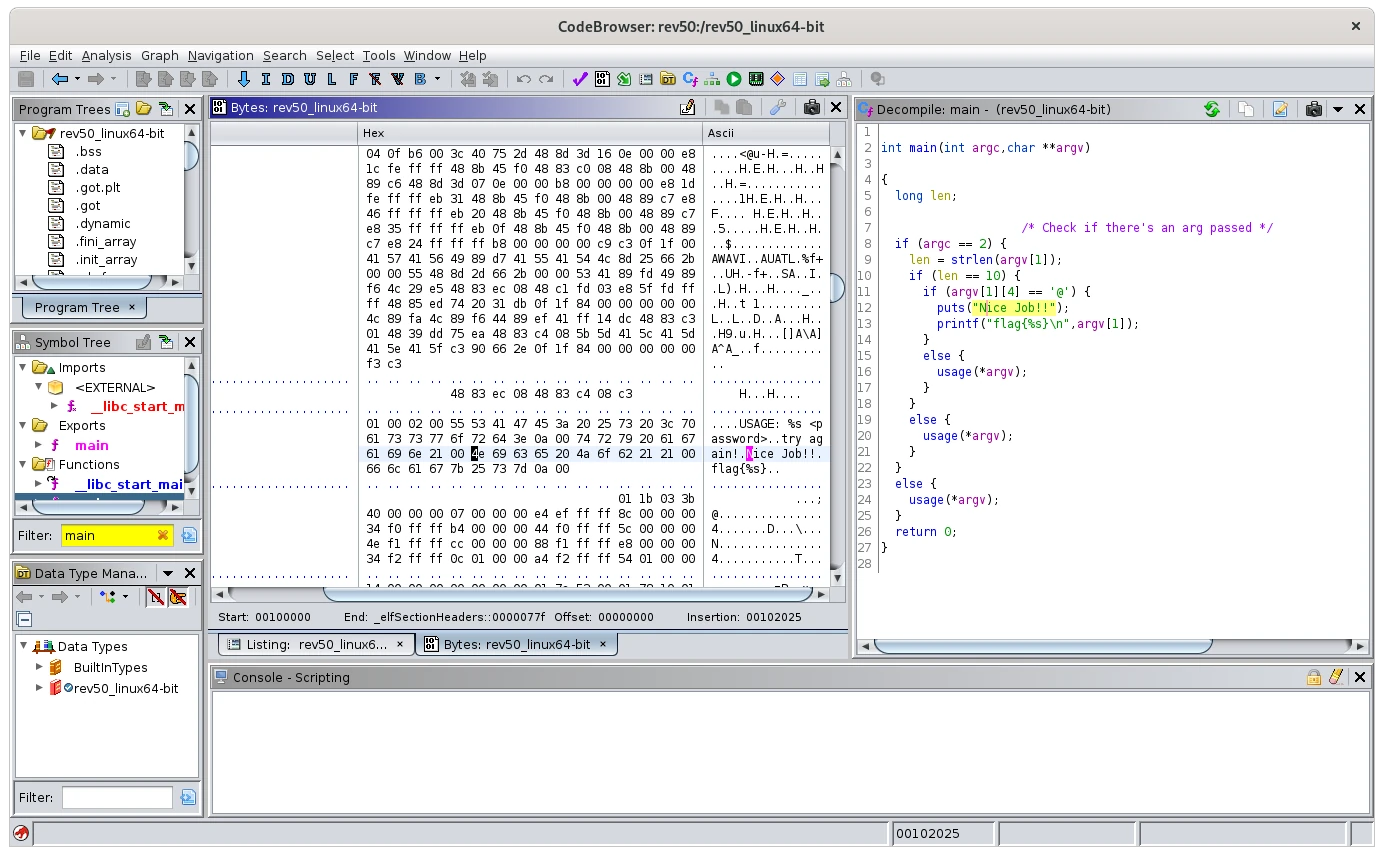
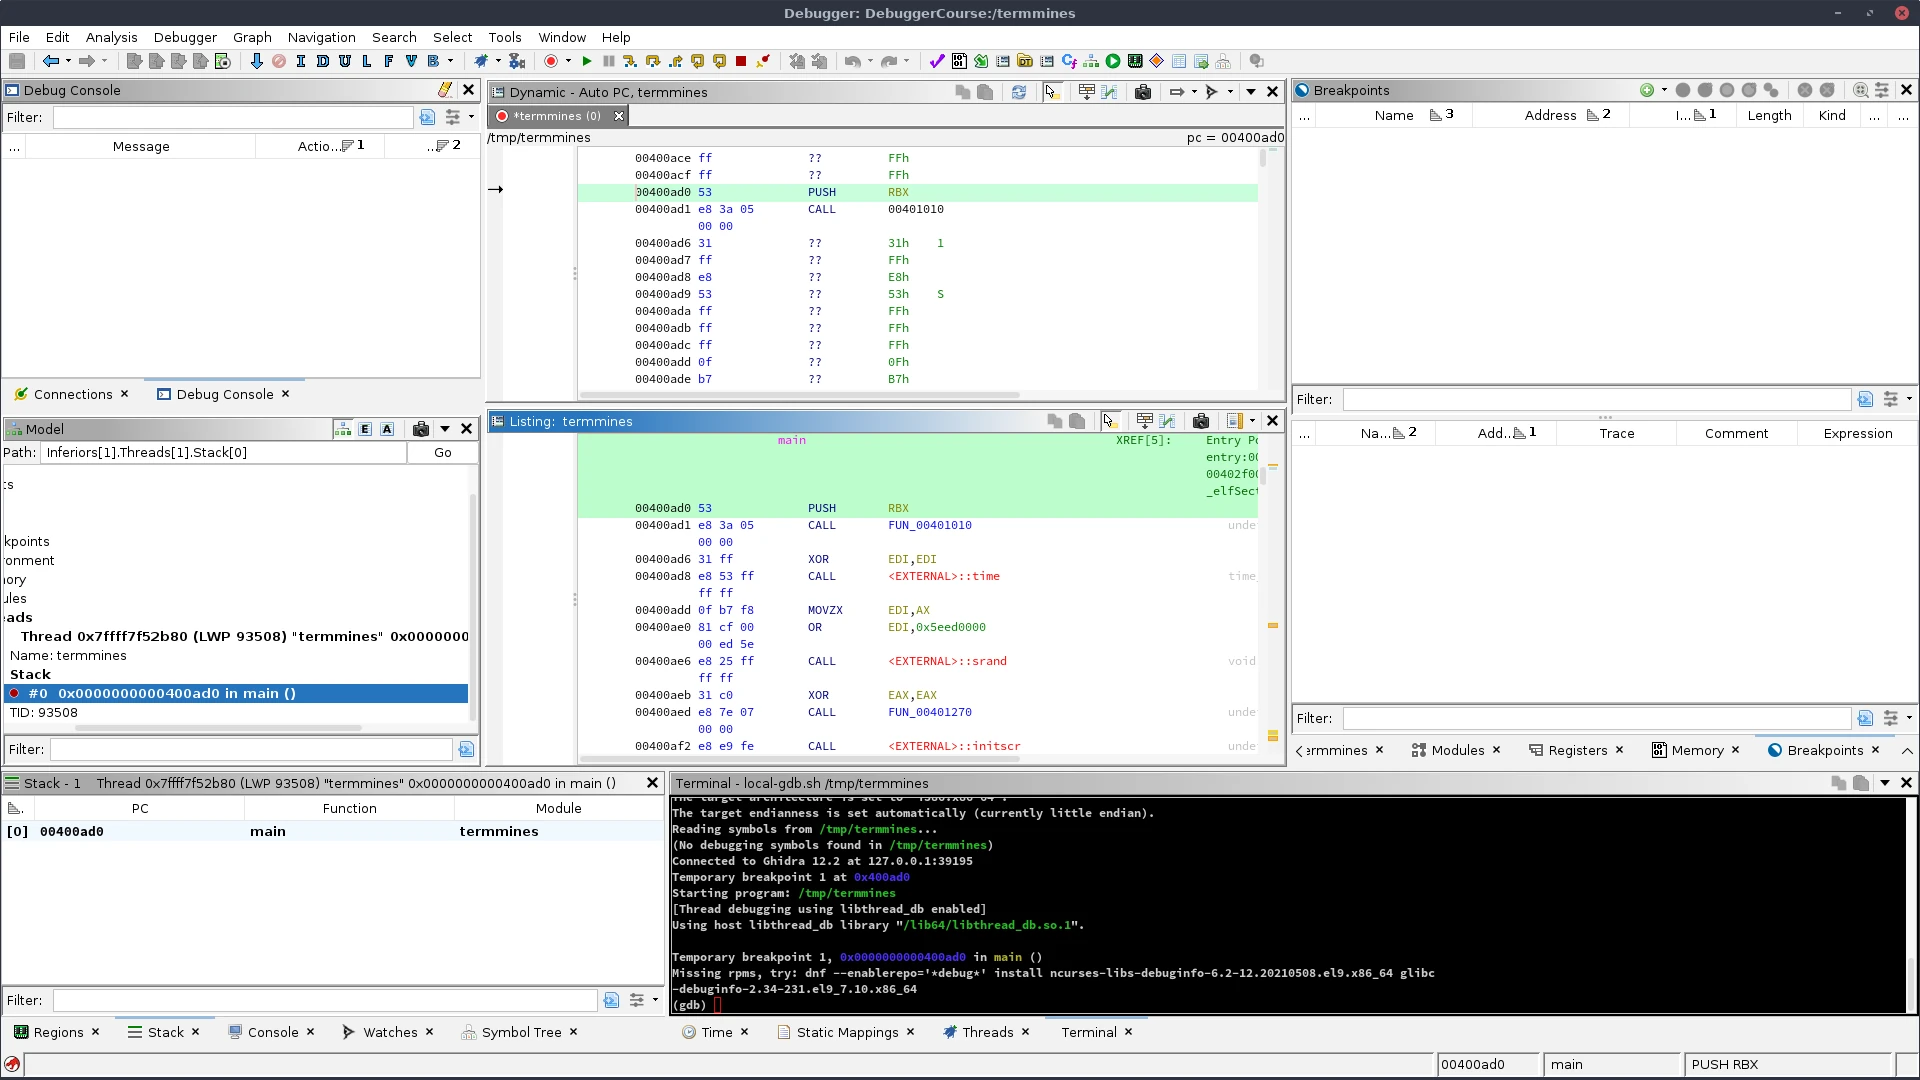
- A genuinely capable decompiler producing C-like output, free and open source
- Very wide processor instruction set and executable format support
- Built for teams, with shared projects and version tracking
- Extensible with Java or Python, and scriptable for automated analysis
|
- Windows only
- Antivirus software frequently flags it and the things it is used on
- PDB symbol support is basic compared with a commercial debugger
- The decompiler is far weaker than Ghidra's or IDA's
|
- The project warns that some versions have known security vulnerabilities
- Java-based, and the interface shows it
- A steep learning curve even for people who know assembly
- Distributed as a portable archive rather than an installer, and needs a JDK
|
|
Downloadable app |
Downloadable app |
|
Open source |
Open source |
|
License: GPL-3.0 |
License: Apache-2.0 |
|
No account needed |
No account needed |
|
Offline features available |
Offline features available |
|
Sources for x64dbg Catalog checked September 21, 2026 |
Sources for Ghidra Catalog checked September 21, 2026 |
“Not stated” means we have not confirmed it. Features can vary by device and plan.
Copy comparison link