

Compare software
  x64dbg |  radare2 |
|---|---|
Screenshots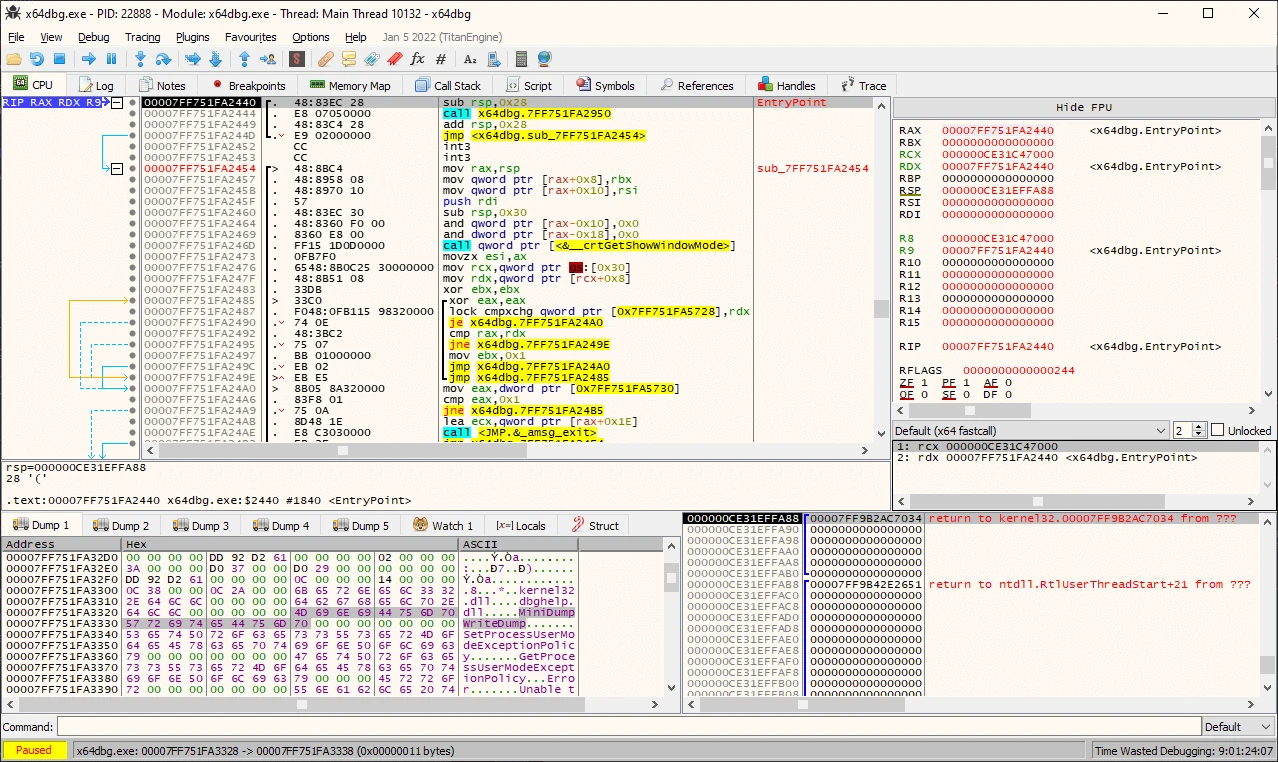 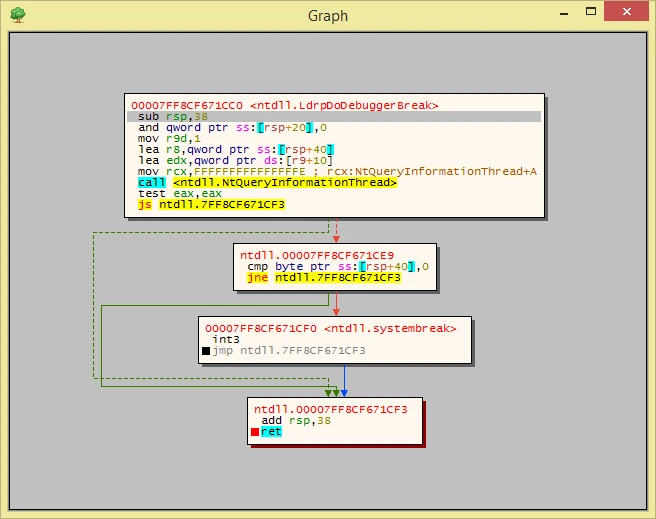  | Screenshots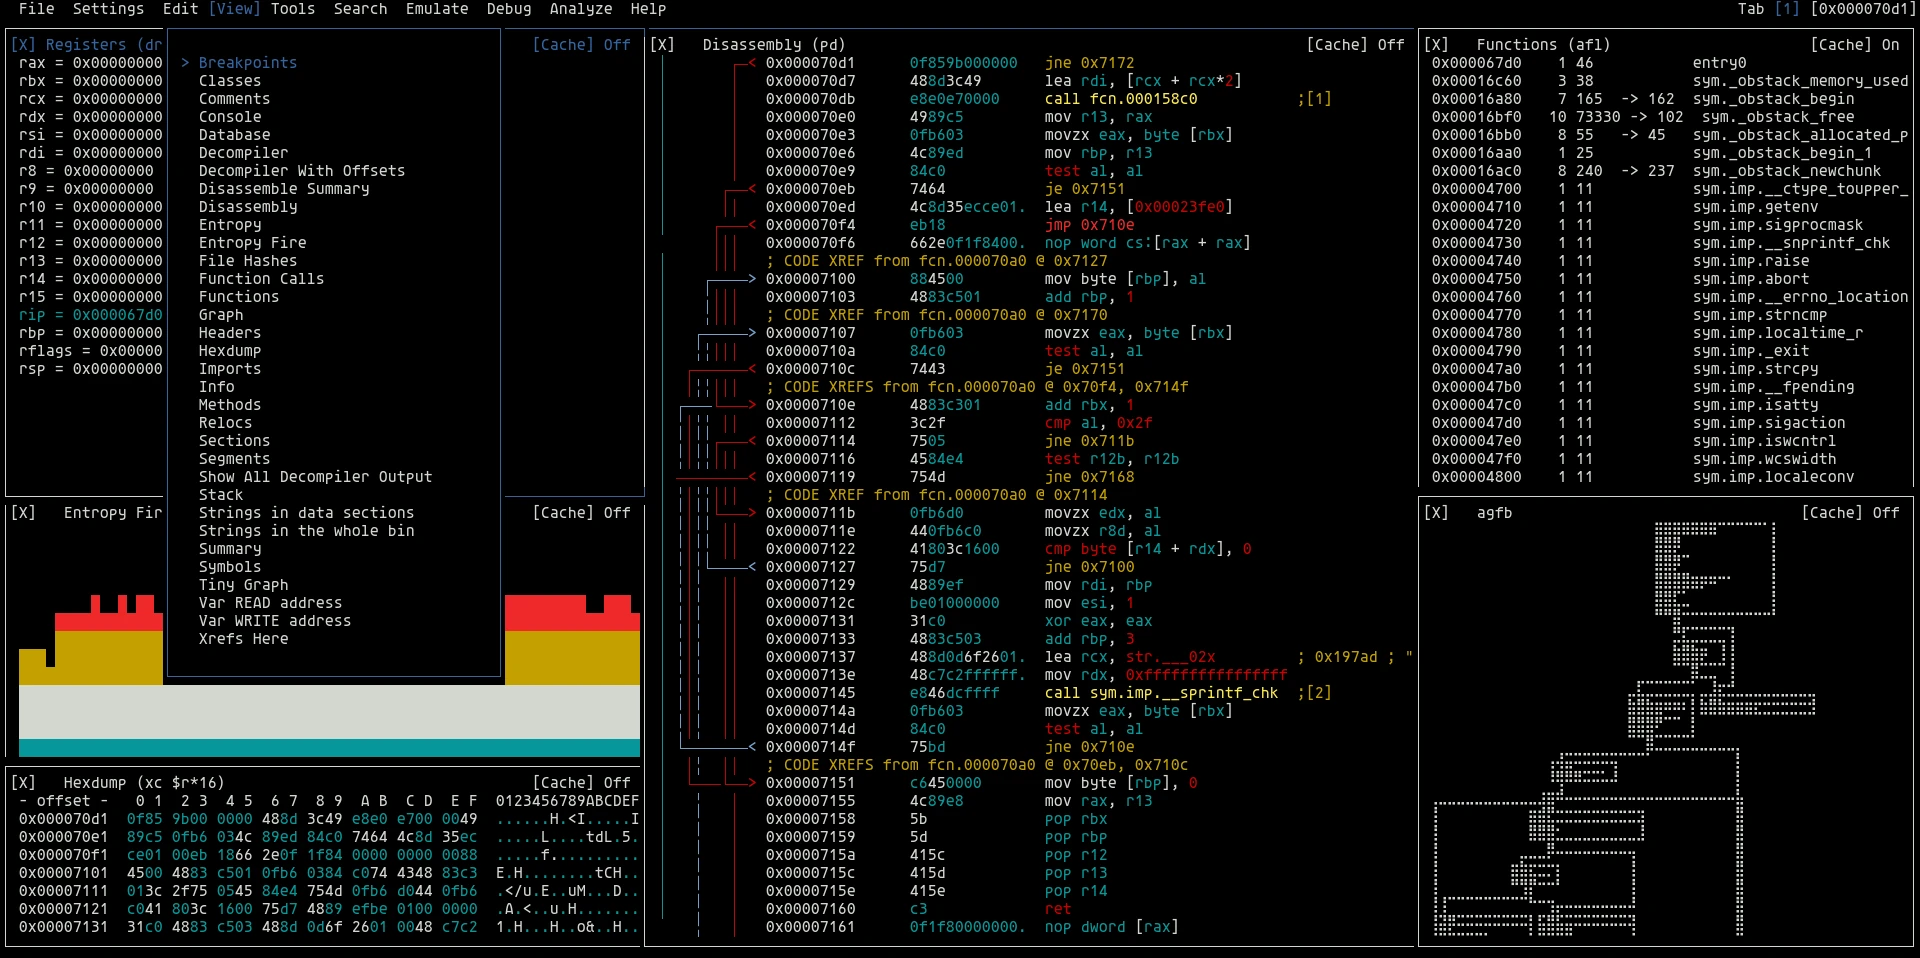 |
|
Best for: Debugging and patching Windows binaries during reverse engineering |
Best for: Command-line reverse engineering framework and binary analysis toolkit |
|
Free Free and open source under the GPLv3. |
Free The software is free under its open-source licence. Hosting, hardware and external services are separate. |
| Windows | Windows, macOS, Linux, Android, Command line |
|
|
|
|
| Downloadable app | Downloadable app |
| Open source | Open source |
| License: GPL-3.0 | License: LGPL-3.0 |
| No account needed | Not stated if an account is needed |
| Offline features available | Not stated if it works offline |
|
Sources for x64dbg Catalog checked September 21, 2026 |
Sources for radare2 Catalog checked September 22, 2026 |
“Not stated” means we have not confirmed it. Features can vary by device and plan.
Copy comparison link